About the client
Our client, the head of security at a financial sector company, shared a real case of detecting an insider within an organization using the INSIDER personnel monitoring and workplace control system.
Task
Starting around September, the renewal rate for the company's products dropped sharply. The quality control department began calling customers to find out who made a better offer. The beneficiary in almost all cases was different. In addition, one of the clients said that he received calls from several organizations at once. Company specialists conducted an internal investigation and found out that one of the employees was selling the database.
The client approached us with the task of finding this attacker.
Process
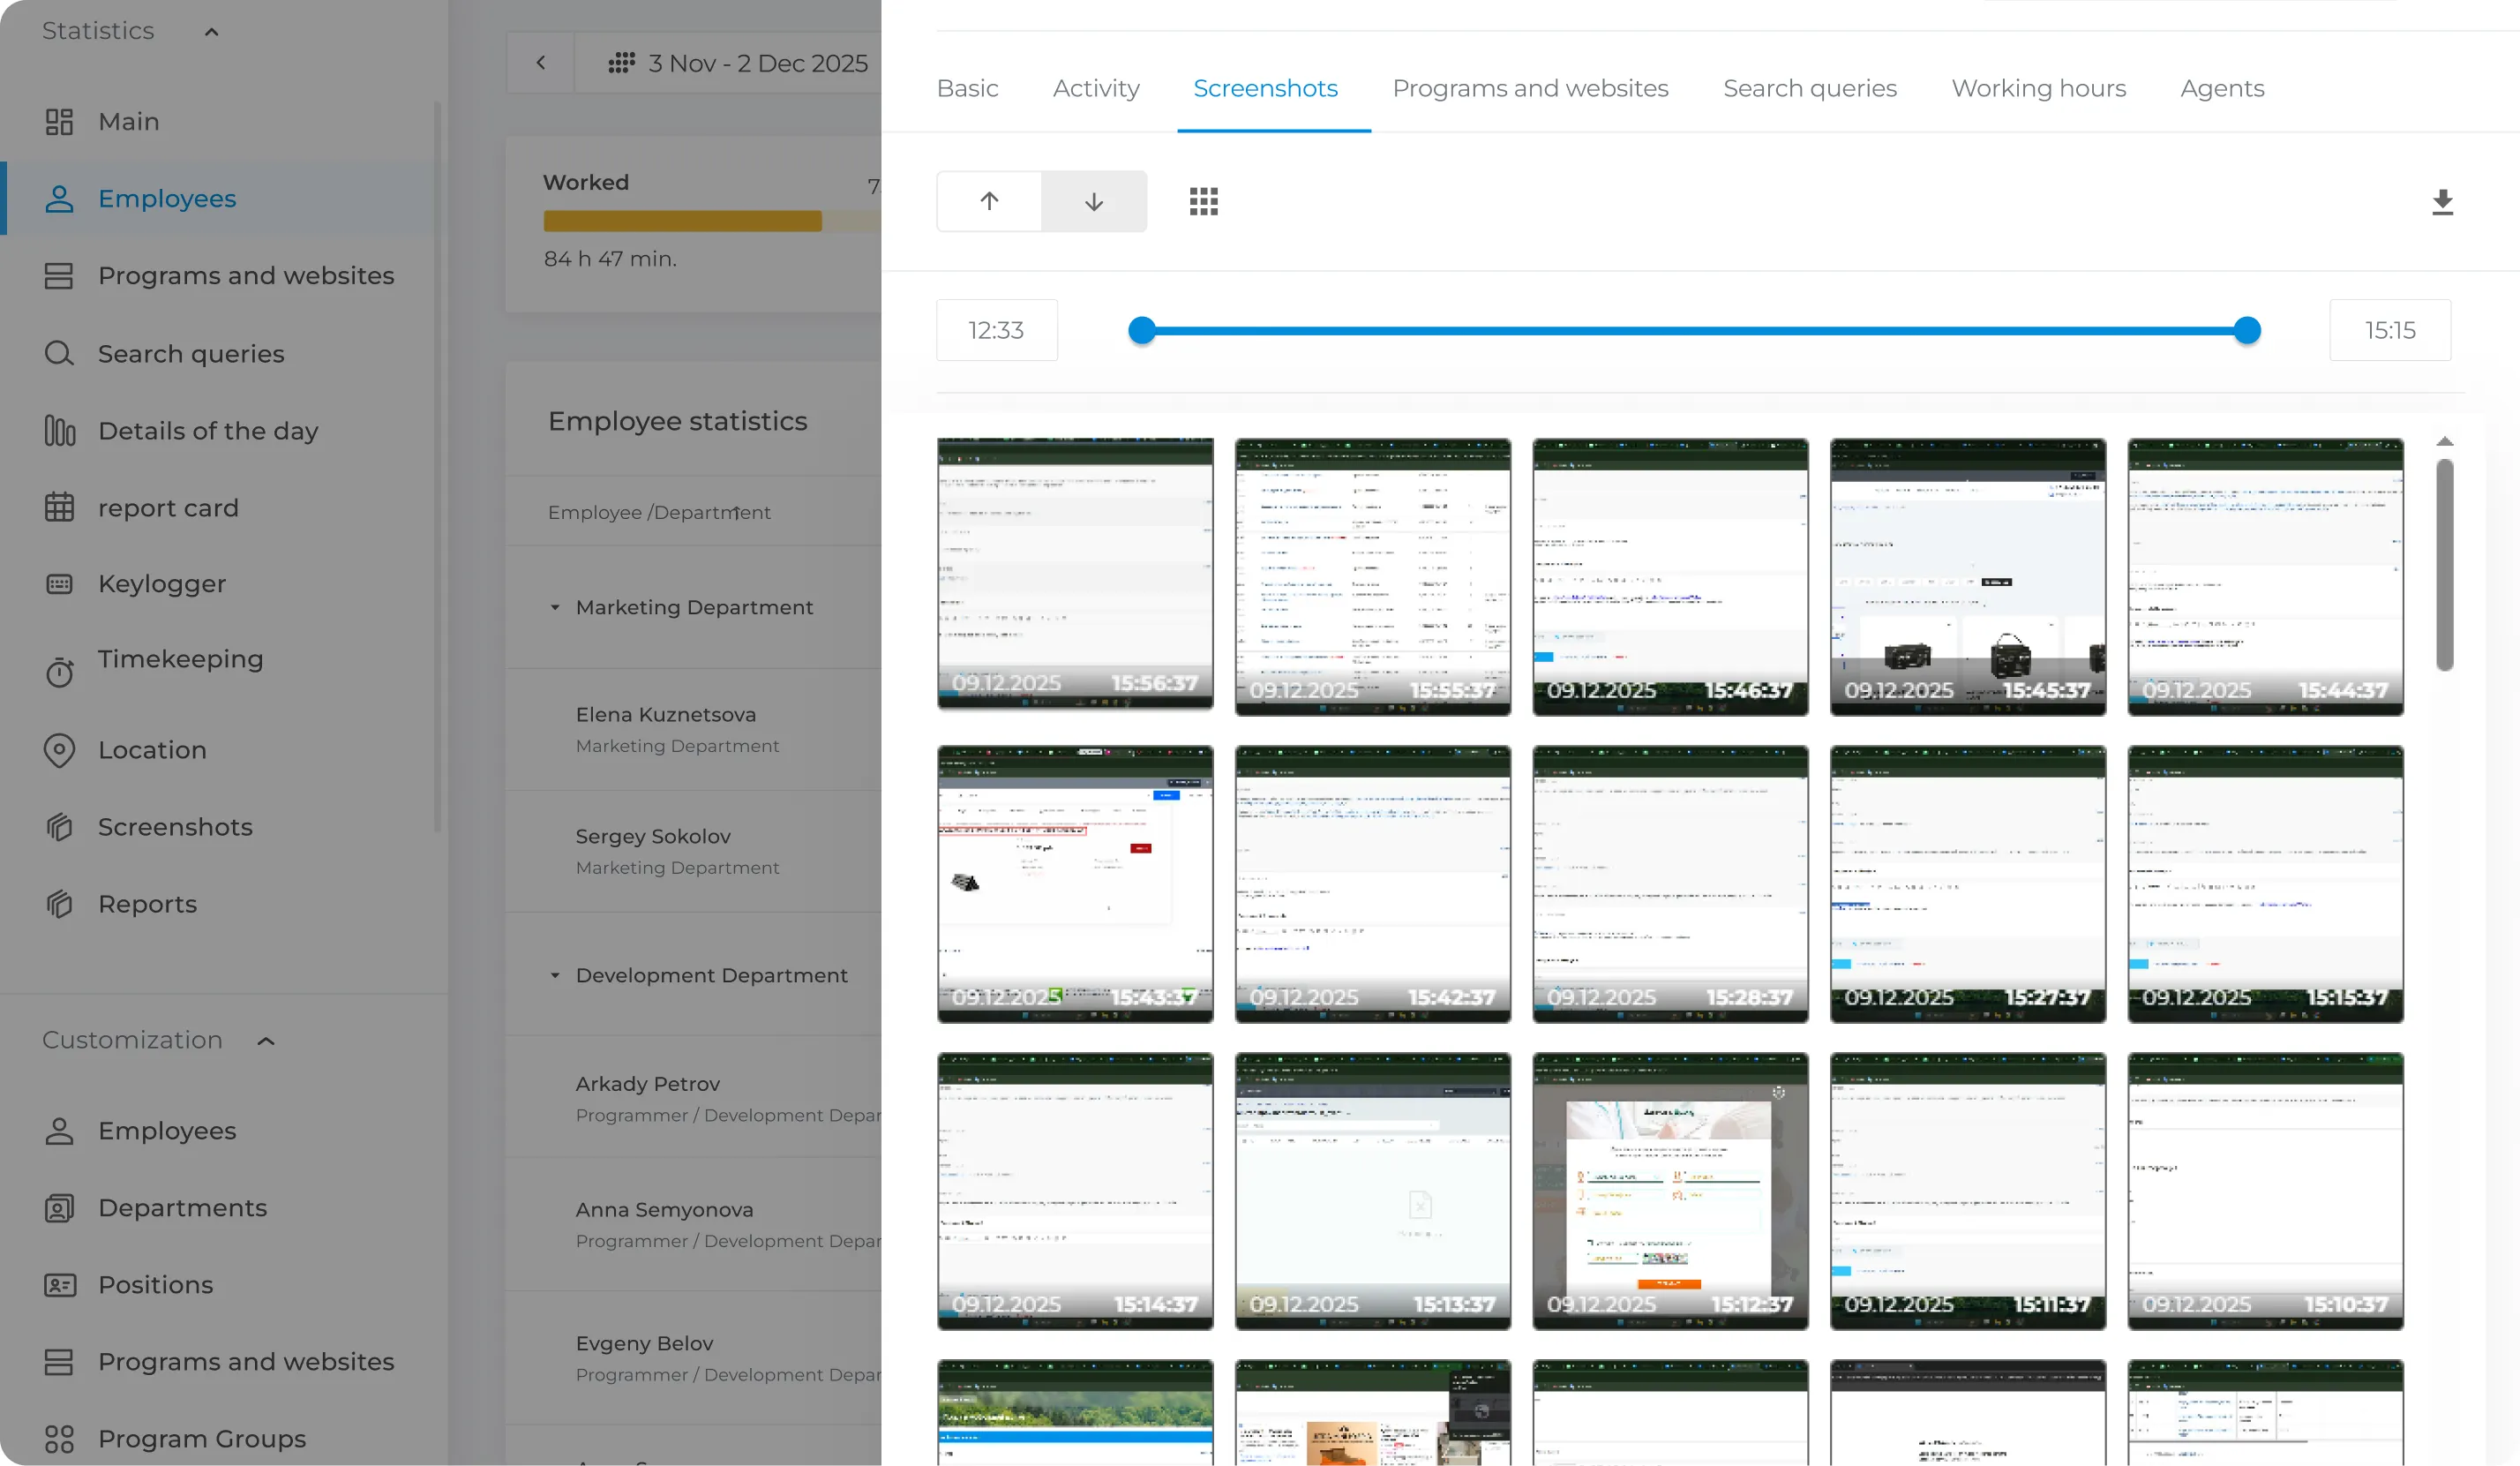
After the above-mentioned incident, it was decided to install the INSIDER system, which could take screenshots of all user actions on the PC and analyze the activity of employees, special attention was paid to those who logged into the CRM.
IN INSIDER you can view the entire history of user interactions with the selected site or program. This ultimately became the decisive factor in catching the attacker. Screenshots of user actions revealed suspicious activity by several employees and recorded the time when it occurred.
It turned out that one of the employees, who did not need the database for work, went into the CRM during lunch break, when no one was in the office, and copied the database page by page.
Result
The attacker no longer works for the company. Of course, the damage caused cannot be repaired, but it was possible to identify a pest that could have done many more dirty tricks.
If you also have interesting stories related to our INSIDER program, send them to us, we will be happy to publish them.